NPMScan
Detect malicious npm packages, crypto-drainers, and vulnerab
Screenshots
 Next.js
 Python
 Postgresql
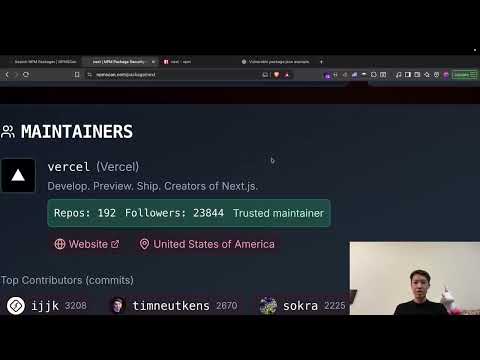
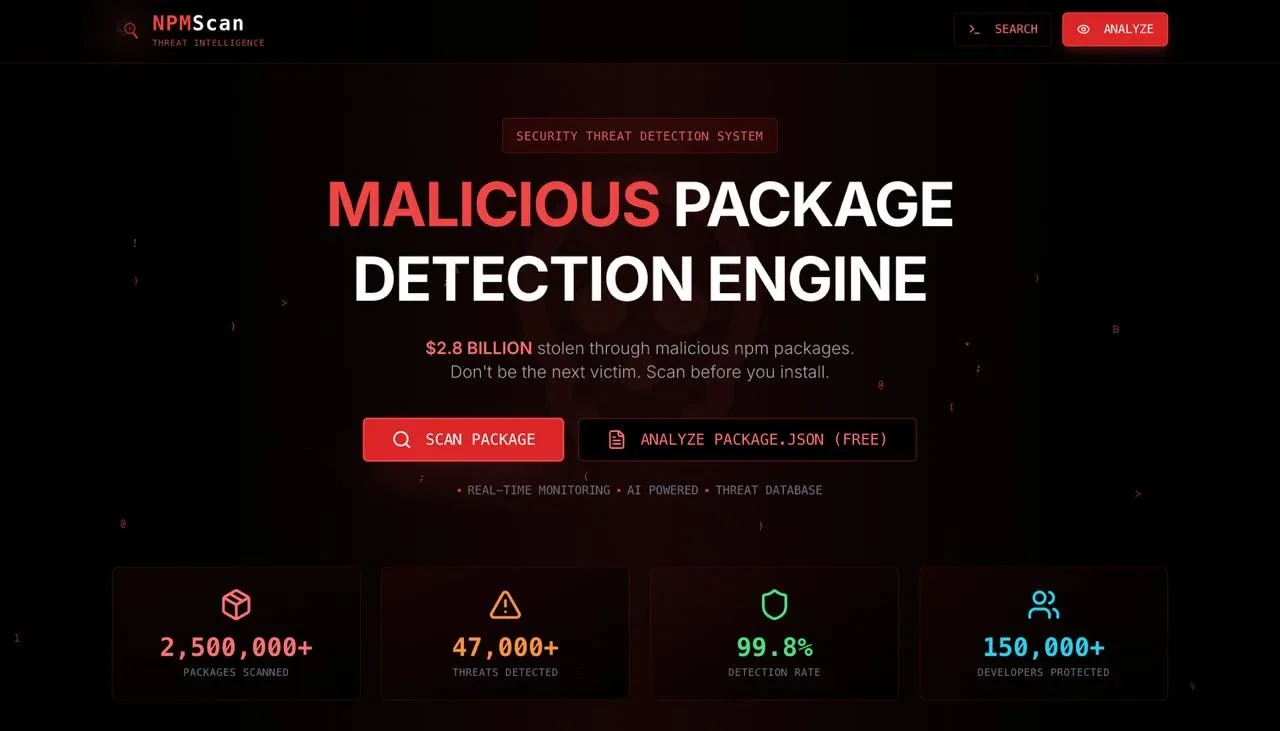
NPMScan is a powerful AI-driven security tool designed to protect Node.js projects from the ever-growing threat of supply chain attacks. It specializes in detecting malicious npm packages, including crypto-drainers, obfuscated code, and other forms of malware that traditional security tools might miss. By focusing on behavioral patterns and heuristic analysis, NPMScan offers a unique layer of defense against novel and sophisticated threats.
The main problem NPMScan solves is the inherent risk associated with trusting third-party npm packages. Developers often face situations where packages appear legitimate but contain hidden malicious code. NPMScan addresses this by providing a quick, accessible, and insightful analysis of packages before they are installed, thereby preventing costly and damaging security breaches.
Key Features:
- Malicious Package Detection: Identifies malware, crypto-drainers, and supply chain abuse patterns.
- AI-Powered Threat Intelligence: Utilizes artificial intelligence to analyze code and detect suspicious behavior.
- Real-time Threat Database: Continuously updated with information on the latest malicious packages.
- Heuristic Analysis: Employs sophisticated heuristics to catch obfuscation, exfiltration attempts, suspicious scripts, and inlined network calls.
- Privacy-First Design: Analyzes packages without storing source code or sensitive project data, ensuring user privacy. Fully GDPR-compliant.
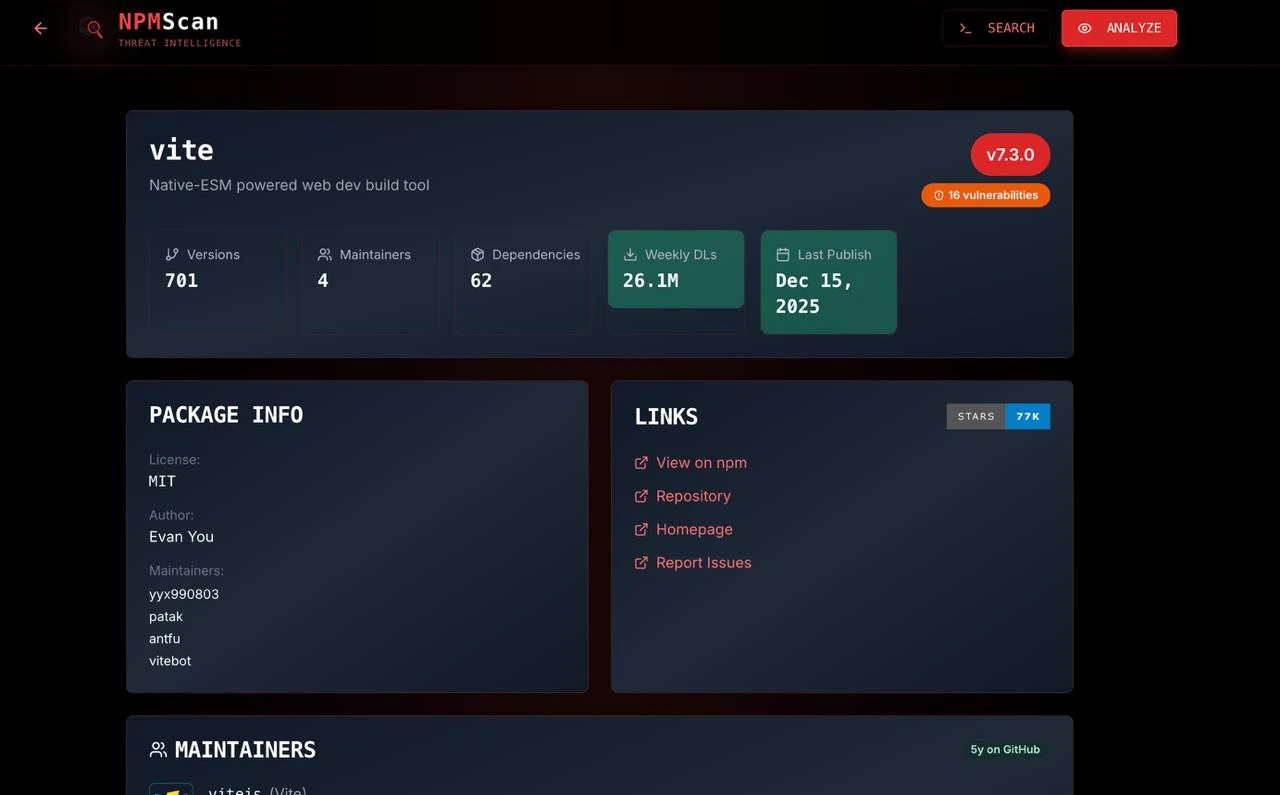
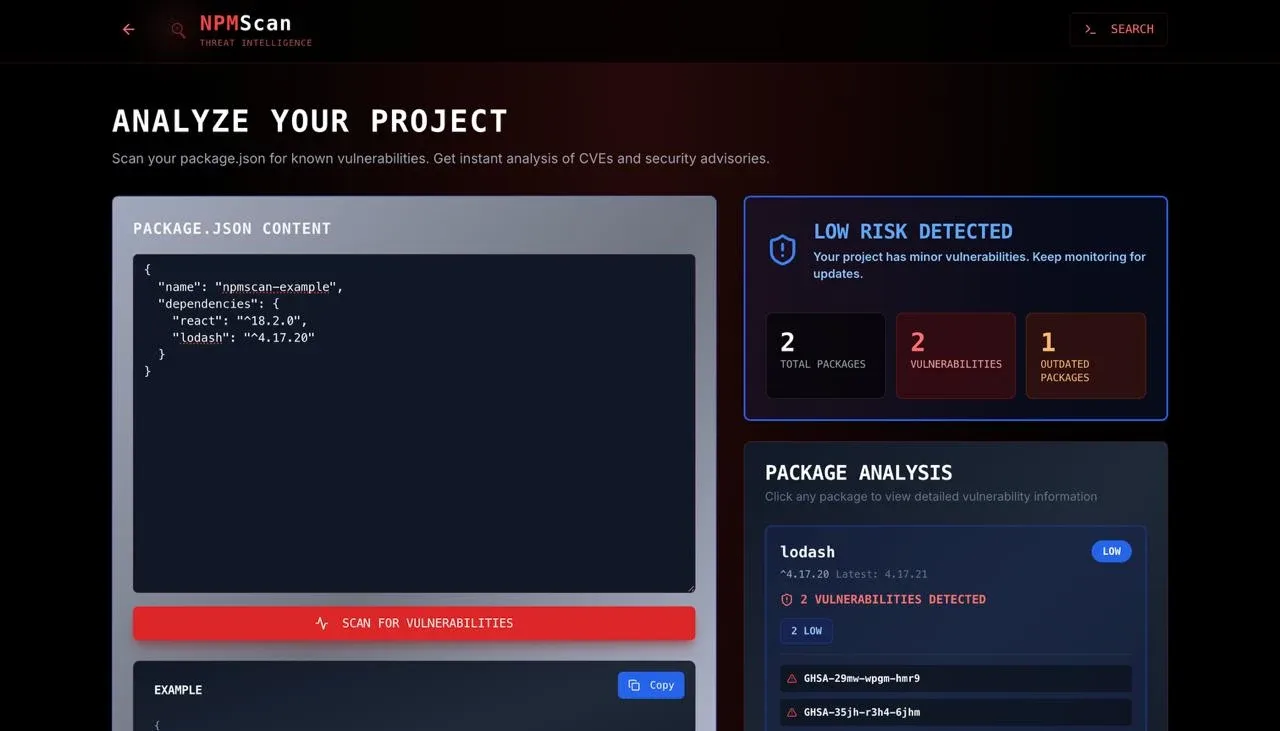
- Instant Risk Summary: Provides a clear and concise risk assessment by simply analyzing package metadata or pasting a package.json file.
- No Install, No Login, No API Keys: Offers immediate usability without complex setup or account creation.
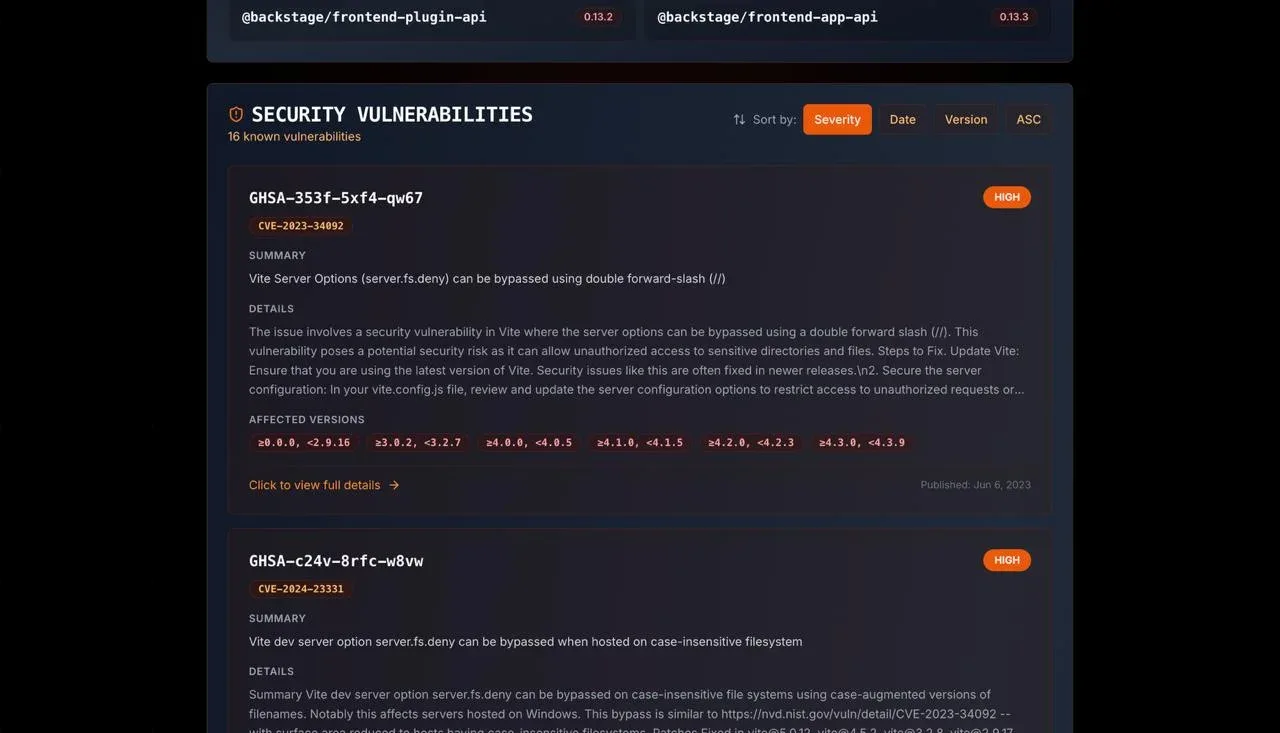
- Comparison to Other Tools: Unlike npm audit or Snyk which focus on known CVEs, NPMScan excels at detecting new, non-CVE malware and malicious behavior.
Who is it for?
NPMScan is ideal for Node.js developers, security professionals, and teams concerned about the security of their software supply chain. It's particularly useful for those who want a quick sanity check on new dependencies or need to identify potential malware that might bypass more traditional vulnerability scanners.
Benefits:
- Prevent Financial Loss: Avoid losses due to crypto-draining and other forms of theft enabled by malicious packages.
- Enhance Security Posture: Add a critical layer of defense against supply chain attacks.
- Save Time: Get rapid analysis without the need for complex installations or configurations.
- Peace of Mind: Quickly verify the safety of npm packages, reducing anxiety about third-party risks.
- Protect Reputation: Safeguard your project and company from the reputational damage associated with a security breach.
NPMScan empowers developers to make informed decisions about the packages they integrate into their projects, fostering a more secure Node.js ecosystem.
Related products
View all
PasteSheet
Turn any Google Sheet into a live REST API and MCP server in

CuteArr
Free QR codes that never expire - no signup, no tracking.
DevCleaner
Reclaim Gigabytes from Your Mac Dev Tools
Ornold
AI-Powered Browser Automation for Antidetect Browsers

More categories
All categories




Launched in Week 51, 2026
See the week
Bringboard
Hiring software that fits your process
AI Site Scorer -
AI SEO readiness checker - MCP for Cursor and agents, x402
The Map Challenge
Put your website on the world map.
NeXaCard
Scan business cards. Save contacts. Never lose the context.